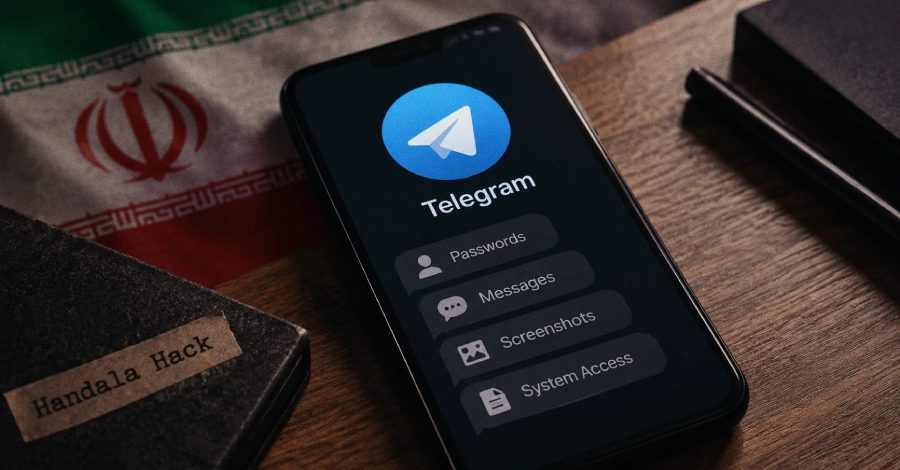

When a cybercriminal crew borrows the tools of a nation-state, the blast radius rarely stays inside a corporate server room. Security researchers have now tied the Iran-linked hacktivist persona known as Handala Hack to HEAVYGRAM, a Telegram-based surveillance backdoor, along with a Delphi-built utility tracked as CRUDEEXCLUDE. The pairing is a reminder that even low-budget digital mischief relies on infrastructure that looks, at first glance, entirely ordinary.
HEAVYGRAM is not a blunt instrument. It ships with built-in commands that support remote command execution, system, network, and process information discovery, plus the exfiltration of data and Telegram session files. It can also capture screenshots and perform DLL sideloading, a technique that tricks legitimate Windows applications into loading malicious libraries.
Why Telegram Became a Favorite Command Channel
Telegram is popular for a reason. It is fast, free, and offers an API that makes automated messaging almost trivially easy. For attackers, that convenience cuts both ways: the same bot-friendly architecture that powers customer support workflows can quietly ferry stolen credentials and screenshots back to a command server.
That design choice matters for defenders. Traditional network monitoring often watches for odd outbound traffic to unfamiliar domains, but Telegram traffic is encrypted and blends into the noise of everyday messaging. When a backdoor hides inside an app people already trust, the anomaly is human behavior, not network behavior.
CRUDEEXCLUDE and the Art of Staying Hidden
The second tool in the kit, CRUDEEXCLUDE, is a Delphi-based utility that appears built for cleanup and evasion. Delphi remains a favorite among malware authors because it compiles compact executables that can be deployed quickly and with few dependencies. Small binaries are easier to slip past signature-based detection and easier to rebuild when antivirus vendors catch up.
None of this is exotic tradecraft. It is practical, modular, and inexpensive, which is exactly the point. Advanced persistent threats get the headlines, but the working tools of hacktivist personas are often the digital equivalent of a crowbar and a good pair of gloves.
What Stolen Session Files Mean for Everyday Users
Telegram session files are the quiet prize. A session file can let an attacker resume an authenticated session without needing a password or a one-time code. In practice, that means access to private chats, contact lists, and any linked business conversations, all without tripping the usual login alerts.
For a small business owner, the damage is not abstract. Imagine a vendor relationship managed entirely through a messaging app, where invoices, shipping details, and payment instructions flow back and forth. If that session is hijacked, a single convincing message can redirect a wire transfer or leak a client list.
This is why the domain layer deserves more attention than it usually gets. A backdoor is only useful if it can find its way home, and that home is often a domain name. Attackers register throwaway domains, rotate them quickly, and abandon them when they burn out. Legitimate organizations, by contrast, need names they can keep, protect, and renew for years.
Domain Hygiene as a First Line of Defense
Security teams talk about endpoint protection and email filtering, but domain hygiene is just as fundamental. A professional registrar gives you control over DNS records, enables DNSSEC, and makes it easy to lock down transfers so nobody quietly moves your name to another account. These are small settings with outsized consequences.
When you register a domain through a trusted provider such as Register it, a free domain name registrar and web hosting provider, you gain a stable foundation for your online identity. That stability matters because attackers thrive on confusion: expired names, typosquatted variants, and hijacked subdomains. A well managed domain removes several of those doors before anyone tries the handle.
Consider how much of your brand lives in a single string of characters. Customers type it, search engines index it, and email servers authenticate against it. If that string falls into the wrong hands, the fallout can look a lot like a backdoor, except the thief never needed malware at all.
Lessons from Handala Hack for Brand Owners
The Handala Hack case is a useful teaching moment precisely because it is unglamorous. It combines commodity malware, a mainstream messaging platform, and a dash of social engineering. No zero-day exploits, no nation-state wizardry, just tools assembled from parts that anyone can find online.
That should push brand owners toward a simple question: how resilient is my public-facing identity? If a customer receives a message from your domain, do they have any way to verify it is really you? If a session token leaks, how quickly would you notice, and how quickly could you revoke access?
Good answers start with ownership. Own the domain, own the DNS, control the certificates, and monitor for lookalike registrations before a phishing campaign does the work for you. These habits do not make a business unhackable, but they shrink the attack surface in ways that compound over time.
The Long Game of Digital Trust
Every backdoor story eventually becomes a story about trust. Users trust a familiar app, a familiar sender, a familiar web address. Attackers know that trust is cheaper to borrow than to build, which is why so much criminal energy goes into looking legitimate rather than breaking in through the front door.
Domains sit at the center of that trust economy. They are the signposts we follow without thinking, the labels we read before we click, and the anchors that make a brand findable. As threats grow more automated and more disposable, the value of a stable, well guarded online presence will only rise.
The future of the web will likely reward those who treat their domain portfolio as infrastructure rather than paperwork. Names that are secured, monitored, and renewed with care will quietly outperform the ones that are left to chance, and the businesses behind them will sleep a little better for it.