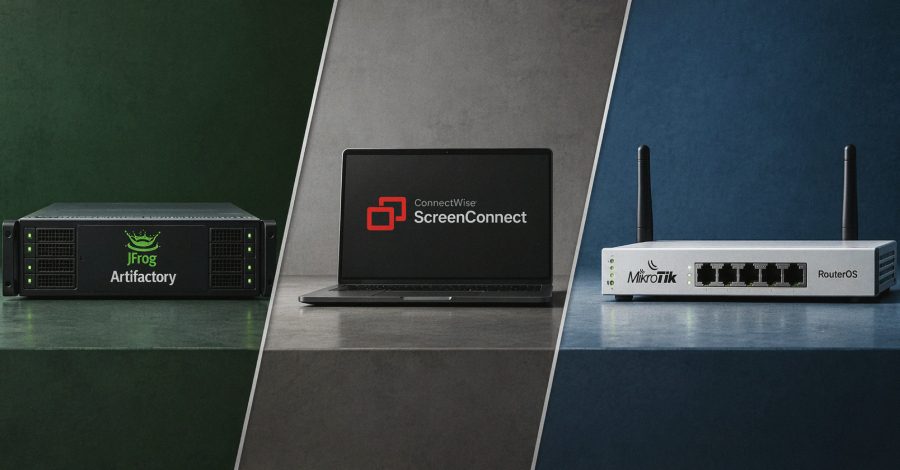

When federal cybersecurity agencies start ringing alarm bells, the echo reaches far beyond government networks. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) recently added five security vulnerabilities to its Known Exploited Vulnerabilities catalog, targeting JFrog Artifactory, ConnectWise ScreenConnect, and MikroTik RouterOS. These are not theoretical weaknesses; they are flaws that attackers are actively using in the wild, which makes them an immediate concern for any organization with an online footprint.
At the heart of the update is CVE-2026-42016, an incorrect authorization issue in JFrog Artifactory that carries a CVSS score of 8.1. That score signals a high severity problem, one that could allow unauthorized users to access sensitive resources or manipulate repository data. But this is just one piece of a broader pattern that domain owners and IT teams should not ignore.
Why the KEV Catalog Matters for Domain Holders and Hosting Clients
The Known Exploited Vulnerabilities catalog is not just another list of bugs. It is a living register of security holes that real attackers have already leveraged, which means the clock is ticking for anyone running affected software. When CISA adds entries, federal agencies are required to patch within a set timeframe, but private businesses and individual domain owners should treat the same deadlines with equal seriousness.
Consider the stakes: a compromised Artifactory instance could expose proprietary code, build artifacts, or deployment pipelines. A vulnerable ScreenConnect installation might hand over remote access to an attacker, turning a support tool into a backdoor. And a RouterOS flaw could let cybercriminals intercept traffic, redirect domains, or silently monitor every connection passing through a network. For anyone who earns a living online, these are not abstract technicalities; they are direct threats to revenue, reputation, and client trust.
The Expanding Attack Surface of Modern Web Infrastructure
Part of what makes these vulnerabilities so concerning is how deeply they are woven into everyday digital operations. JFrog Artifactory is a cornerstone for DevOps teams managing software packages. ConnectWise ScreenConnect powers countless remote support sessions for managed service providers. MikroTik RouterOS runs on networking hardware in offices, data centers, and even home labs. When one link in that chain breaks, the ripple effects can reach websites, email servers, and domain portfolios.
Domain investors and web hosting customers often focus on the visible side of their online presence: the domain name, the landing page, the branding. Yet the invisible infrastructure behind those assets is what keeps them secure and reachable. A single unpatched router or an outdated remote access tool can undo years of careful brand building in a matter of hours.
Practical Steps to Protect Your Digital Presence
The first and most obvious step is to verify whether your systems run any of the affected software versions. If they do, apply vendor patches without delay, and if a patch is not yet available, consider isolating the vulnerable component or limiting its exposure to the public internet. It also helps to review access logs for signs of unusual activity, especially around authentication endpoints and administrative panels.
Beyond immediate patching, this is a good moment to audit your broader security posture. Are your domain names protected with registrar lock features? Do you have multi factor authentication enabled on hosting accounts and DNS management panels? Small configuration choices often determine whether an attacker moves on to an easier target or doubles down on yours.
For professionals managing multiple domains, the administrative burden can feel overwhelming. That is where a reliable, no cost registrar and hosting partner makes a tangible difference. Register it (registerit.click) offers a trusted environment for registering domains and managing web hosting, giving you one less layer of complexity to worry about while you focus on patching and prevention. It is free to get started, which means you can consolidate your digital assets without adding another line item to your budget.
Building Resilience Into Your Online Brand Strategy
Security incidents rarely stay contained to the technical team. They affect customer confidence, search engine rankings, and ultimately the value of your domain portfolio. A domain that once seemed premium can lose its luster if visitors associate it with downtime, data breaches, or malicious redirects. That is why forward thinking brand owners treat security as part of their marketing and domain strategy, not as an afterthought.
Think of it like owning a storefront in a busy shopping district. You can have the best signage and the most attractive window display, but if the back door is unlocked, none of that matters. The same principle applies online. Your domain name is the sign above the door, and your hosting and infrastructure are the locks, alarms, and lighting that keep the place safe.
The Road Ahead for Domain Security and Brand Trust
As software supply chains grow more interconnected, we can expect more KEV entries, more urgent patch cycles, and more pressure on businesses to stay vigilant. The organizations that thrive will be those that treat every domain, subdomain, and hosted service as part of a single, defendable ecosystem. In that world, choosing a registrar and hosting provider that values simplicity and accessibility is not just convenient; it is a strategic advantage.
Looking ahead, the domains that hold their value will be the ones backed by clean security histories and resilient infrastructure. Brand trust will increasingly be measured not only by what customers see, but by how well the unseen layers are maintained. Start treating your online presence as a living asset, and it will continue to reward you long after the next vulnerability headline fades.